

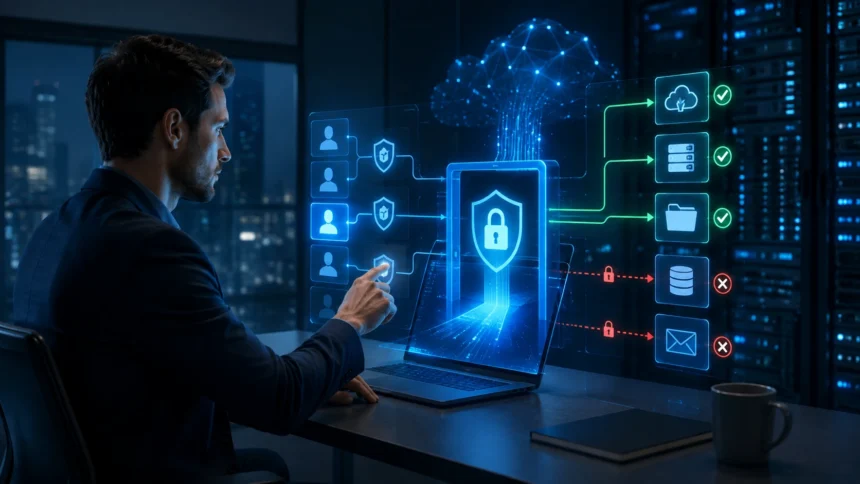
AuthZ Explained: What It Is & How Authorization Works
Every time you open a company dashboard, access a cloud application, edit a document, or call an API, a security decision happens behind the scenes. The system must determine not only who you are, but also what you are allowed to see, change, download, delete, or share. That decision-making process is known as authorization, commonly shortened to AuthZ.
AuthZ is one of the most important parts of modern identity and access management. Authentication may confirm that a user is legitimate, but authorization decides what that authenticated user can actually do. Without strong authorization controls, someone could successfully log in and still gain access to information or functionality that should remain restricted.
Modern authorization has become more important as organizations adopt cloud platforms, SaaS applications, APIs, microservices, remote work, and distributed infrastructure. Access decisions are no longer limited to whether someone can enter an application. Systems increasingly need to evaluate roles, resources, device conditions, data sensitivity, location, ownership, and contextual security signals.
Understanding how AuthZ works helps developers, cybersecurity professionals, IT teams, and everyday technology users understand how digital access is controlled. From role-based permissions to OAuth scopes and Zero Trust policies, authorization provides the rules that determine who can do what within a digital environment.
What Is AuthZ?
AuthZ is a commonly used abbreviation for authorization, the security process that determines whether a user, application, device, or service has permission to perform a specific action on a particular resource. It typically takes place after an identity has been authenticated or otherwise established.
For example, a company application may recognize that you are an authenticated employee. AuthZ determines whether you are allowed to view customer records, update financial information, access administrator settings, approve transactions, or download confidential reports based on the permissions assigned to you.
Authorization decisions can be simple or highly detailed. A small application might only distinguish between ordinary users and administrators, while an enterprise system may evaluate roles, departments, resource ownership, subscription plans, geographic restrictions, security posture, and hundreds of policy conditions.
The purpose of AuthZ is therefore not simply to keep unauthorized people out of a system. It controls what legitimate identities can access after they enter, helping organizations reduce unnecessary privileges and protect sensitive resources from accidental or intentional misuse.
How Does Authorization Work?
Authorization begins when a subject such as a user or application attempts to perform an action. The requested action might involve reading a file, updating a database record, deleting an account, changing configuration settings, or calling a protected API endpoint.
The system then examines available authorization information. This may include the user’s role, group membership, attributes, permissions, OAuth scopes, ownership relationships, resource characteristics, security policies, and environmental context surrounding the access request.
An authorization engine or application logic compares the request against established access-control rules. If the relevant policy allows the action, access is granted. If the necessary permissions are missing or a policy explicitly prohibits the request, the system denies access.
This process can happen extremely quickly and may occur repeatedly during a single session. Logging into an application once does not mean every later action is automatically permitted. Sensitive operations can trigger new authorization checks whenever protected resources are requested.
AuthZ vs AuthN: What Is the Difference?
AuthN, short for authentication, answers the question, “Who are you?” It verifies identity using methods such as passwords, passkeys, biometrics, security keys, certificates, or multi-factor authentication before allowing someone to establish a trusted session.
AuthZ, on the other hand, answers the question, “What are you allowed to do?” Once the system understands the identity involved, authorization determines which applications, files, APIs, records, features, or administrative functions that identity may access.
Imagine entering a secured office building. Showing your employee badge at the entrance resembles authentication because it confirms your identity. Whether that same badge unlocks the finance department, server room, executive floor, or particular storage cabinets is closer to authorization.
The two processes work closely together but solve different security problems. Strong authentication without proper authorization may still expose sensitive resources, while detailed permissions provide little protection if attackers can easily impersonate legitimate users.
Why AuthZ Matters for Modern Cybersecurity
Modern applications frequently store sensitive personal, business, financial, operational, and customer information. Authorization helps ensure that access to these resources is limited to the people and systems that genuinely need them to perform legitimate tasks.
Poor authorization can allow users to access data belonging to other accounts, invoke administrative functions, change protected settings, or retrieve information that should remain restricted. These problems may exist even when authentication itself is functioning correctly.
Authorization has become particularly important as technology environments become more distributed. A user might interact with SaaS tools, internal services, public APIs, cloud databases, microservices, mobile applications, and third-party platforms during a single business workflow.
Strong AuthZ creates boundaries throughout those environments. Instead of assuming that authenticated users should automatically be trusted, organizations can evaluate individual requests and provide only the level of access necessary for a particular identity, resource, and situation.
What Is Access Control?
Access control is the broader security practice of regulating who or what can interact with protected resources. Authorization is a core part of access control because it evaluates whether a requested operation satisfies the organization’s established access rules.
Resources can include files, databases, APIs, applications, cloud infrastructure, administrative panels, devices, business records, and individual pieces of information. Access control determines which subjects can perform actions such as viewing, creating, editing, approving, executing, or deleting those resources.
Effective access control usually combines identities, permissions, policies, and enforcement mechanisms. Instead of relying on one universal rule, organizations can create different access levels based on employee responsibilities, system requirements, resource sensitivity, and security risk.
Modern access control is also increasingly dynamic. A request that would normally be permitted may be denied when it originates from an unmanaged device, suspicious location, expired session, unusual network, or other context that increases security risk.
How Permissions Work in Authorization
A permission represents an allowed action that an identity can perform within a system. Common permissions include read, write, edit, create, delete, share, export, approve, configure, manage users, or execute administrative operations.
Applications can assign permissions directly to individual users, although doing so becomes difficult to manage at scale. Larger organizations usually group permissions through roles, policies, groups, attributes, or entitlement systems that simplify access administration.
Permissions should also be sufficiently specific. Instead of providing a broad “administrator” privilege whenever someone needs one additional feature, well-designed systems can grant narrower permissions covering only the functions required for the person’s responsibilities.
Granular authorization reduces unnecessary access and limits potential damage when accounts are compromised. It also helps organizations understand who can perform sensitive actions, making security reviews, audits, compliance efforts, and access investigations more manageable.
What Is Role-Based Access Control?
Role-Based Access Control, or RBAC, grants permissions according to predefined roles. Instead of assigning every permission separately to every user, administrators create roles such as employee, manager, finance analyst, support agent, developer, or administrator.
Each role contains permissions related to the responsibilities associated with that position. A support agent may be able to view customer profiles and update support tickets, while a finance role may access invoices, payment reports, and accounting-related systems.
Users can then be assigned one or more appropriate roles. This model makes authorization easier to manage because changing a role’s permissions can update access for many users rather than requiring administrators to modify every account individually.
RBAC works particularly well when responsibilities are predictable and stable. However, organizations with complex resource relationships or highly contextual access requirements may combine role-based authorization with attributes, policies, or other access-control models.
What Is Attribute-Based Access Control?
Attribute-Based Access Control, commonly called ABAC, makes authorization decisions based on attributes associated with users, resources, actions, and the surrounding environment. These attributes provide more detailed context than a traditional role alone.
A policy might allow employees in the legal department to access a document only when its classification is appropriate, the request originates from a managed device, and access occurs within an approved geographic region.
ABAC can therefore support highly flexible access policies. Organizations may evaluate department, job title, employment status, data classification, ownership, device posture, risk level, time of day, network location, and many other contextual characteristics.
The flexibility of ABAC is powerful but can make policy design more complicated. Organizations need consistent attribute data, understandable policy rules, reliable enforcement, and strong testing to prevent unexpected access from complicated or conflicting conditions.
RBAC vs ABAC: Which Authorization Model Is Better?
RBAC is often easier to understand because access is grouped around recognizable organizational roles. For environments with clearly defined responsibilities, role-based authorization can provide a straightforward way to grant and review permissions.
ABAC provides greater flexibility because decisions can respond to contextual information rather than relying only on static roles. It can be useful when access requirements depend on resource sensitivity, location, device status, ownership, business unit, or changing security conditions.
Neither model is universally better. Many modern organizations combine them, using roles to establish general permissions and attributes or policies to determine whether particular actions should be allowed in specific circumstances.
The right approach depends on application complexity, organizational structure, compliance obligations, security requirements, and the number of resources being protected. The objective should remain consistent: users receive enough access to do their work without receiving unnecessary privileges.
What Is Policy-Based Access Control?
Policy-Based Access Control, sometimes called PBAC, uses centrally defined policies to determine whether access requests should be approved. Instead of embedding every authorization decision directly into application code, rules can be defined and managed as security policies.
A policy might state that only approved finance employees can export payment information, that customer records can only be edited by their assigned account teams, or that production systems require stronger authorization conditions than development environments.
Centralized policies can make authorization easier to understand across distributed applications. Developers can focus on requesting authorization decisions while dedicated policy systems determine whether the relevant identity, action, resource, and context satisfy the organization’s rules.
Policy-driven authorization is especially useful in cloud-native and microservices environments where many services require consistent security decisions. Centralized policy logic can reduce duplicated authorization code while helping teams apply access rules more consistently across systems.
The Principle of Least Privilege in AuthZ
The principle of least privilege means giving users, applications, and services only the permissions they need to perform their legitimate responsibilities. Additional privileges should not be granted simply because they might become useful someday.
For example, an employee who only needs to view customer records should not automatically receive permission to delete them. Similarly, an application that only reads information from cloud storage should not receive unnecessary write or administrative privileges.
Least privilege limits the impact of mistakes, compromised accounts, malicious insiders, and vulnerable applications. If an attacker gains control of an account with restricted permissions, the number of systems and resources they can potentially affect is reduced.
Maintaining least privilege requires ongoing effort because access tends to accumulate over time. Organizations should regularly review roles, permissions, service accounts, API scopes, temporary access, and unused privileges to ensure authorization remains aligned with current responsibilities.
What Are Authorization Policies?
Authorization policies are rules that define the conditions under which a specific action should be allowed or denied. These policies convert organizational security requirements into decisions that software and infrastructure can enforce.
A simple policy might state that only administrators may delete accounts. A more contextual policy might allow database changes only from authorized engineering accounts using managed devices during an approved maintenance window.
Policies may include subjects, resources, actions, and environmental conditions. The more complex an application becomes, the more important it is to define these relationships clearly so developers and security teams understand exactly why particular requests succeed or fail.
Good policies should also follow a deny-by-default philosophy where appropriate. Instead of assuming unknown actions are permitted, systems can explicitly allow approved behavior while denying operations that do not satisfy defined authorization requirements.
How AuthZ Works in Identity and Access Management
Identity and Access Management, or IAM, combines processes and technologies used to manage digital identities and their access to organizational resources. Authorization plays a central role because IAM systems frequently assign roles, permissions, groups, and entitlements.
When an employee joins an organization, IAM processes may create accounts and provide access according to their role. When responsibilities change, authorization assignments should be adjusted so the employee gains required permissions and loses access they no longer need.
IAM also becomes important when employees leave an organization. Access should be revoked promptly across applications, cloud environments, collaboration tools, databases, and other resources to prevent former users from retaining active privileges.
Well-managed IAM therefore supports the full authorization lifecycle. Instead of treating permissions as permanent settings, organizations can govern access from initial provisioning through role changes, periodic reviews, temporary elevation, and eventual account deactivation.
What Are Entitlements in Authorization?
An entitlement represents a specific access right or capability assigned to an identity. Depending on the system, an entitlement may provide access to an application, database, folder, feature, administrative capability, cloud resource, or business process.
Entitlements can be assigned directly or inherited through roles, groups, subscriptions, or organizational policies. In large enterprises, one employee may have many entitlements across dozens of applications and infrastructure platforms.
Managing these permissions becomes challenging when organizations cannot easily determine why access was granted. Clear entitlement ownership and regular reviews help teams identify excessive, unused, duplicate, or inappropriate access before it creates unnecessary security exposure.
Modern identity governance programs often focus heavily on entitlement visibility. Understanding not only which users exist but also exactly what those users can access is essential for maintaining effective authorization across complicated technology environments.
How OAuth Uses Authorization
OAuth is an authorization framework commonly used to allow applications to access resources on behalf of users or other applications without requiring them to directly share account passwords with the requesting software.
For example, a third-party application might request permission to access certain account information from another service. Instead of receiving the user’s login credentials, the application receives an access token representing the authorization it has been granted.
OAuth commonly uses scopes to describe the level or type of requested access. One scope might allow reading profile information while another allows creating or modifying particular resources, depending on how the service defines its authorization model.
OAuth itself should not be confused with authentication. Technologies can use OAuth alongside identity protocols, but its core purpose is delegated authorization: deciding what an application may access and providing a controlled mechanism for exercising those permissions.
What Are OAuth Scopes?
An OAuth scope defines a particular category of access that an application can request. Scopes help services avoid issuing tokens with unlimited capabilities when an application only needs permission to perform a small number of actions.
For instance, an application might request permission to read calendar information without receiving permission to delete events. Another application may need access to basic profile information but should not have access to messages, documents, or administrative settings.
Well-designed scopes improve security by supporting least privilege. Applications should request only the permissions necessary for their intended functionality, while users and administrators should understand the access being granted before approving sensitive scopes.
Scopes alone do not replace application-level authorization. Even when a token includes an appropriate scope, the receiving service may still need to verify ownership, tenant boundaries, resource relationships, role permissions, and additional security policies.
How API Authorization Works
Modern API authorization determines whether a client is permitted to perform requested operations through an application programming interface. APIs frequently expose sensitive business functions, making authorization essential for preventing inappropriate access.
An API may receive an access token containing identity information, scopes, roles, or claims. The service evaluates this information together with the requested endpoint and resource before deciding whether the operation should be permitted.
Secure APIs should check authorization at the resource level rather than assuming that access to an endpoint automatically grants access to every object behind it. A user permitted to view their own account, for example, should not automatically be able to retrieve another customer’s account by changing an identifier.
This distinction has become increasingly important as applications expose more functionality through APIs. Strong object-level and function-level authorization helps prevent users from manipulating requests to reach data or capabilities outside their legitimate permissions.
What Is Broken Access Control?
Broken access control occurs when an application fails to enforce authorization rules correctly. Users may then be able to access resources or perform operations that should have been restricted by roles, permissions, ownership, or security policies.
A common example occurs when changing an identifier in a request allows someone to view another user’s information. Other problems include accessing administrative endpoints, modifying protected fields, bypassing permission checks, or performing privileged operations from ordinary accounts.
These vulnerabilities can be particularly serious because attackers may not need to defeat the login process. They can authenticate normally and then exploit missing or inconsistent authorization checks to reach information belonging to other users or obtain additional privileges.
Developers should therefore treat authorization as a server-side security requirement. Hiding buttons or menu items in the user interface is not sufficient because attackers can modify requests and attempt to access protected functionality directly.
What Is Privilege Escalation?
Privilege escalation happens when a user, application, or attacker gains permissions beyond the level they were originally authorized to possess. This can occur because of software vulnerabilities, incorrect configurations, overly broad roles, or authorization flaws.
Vertical privilege escalation occurs when a lower-privileged identity gains higher-level capabilities, such as an ordinary user reaching administrator functionality. Horizontal privilege escalation occurs when someone accesses resources belonging to another user with a similar privilege level.
Both forms can have serious consequences. Unauthorized privileges may allow attackers to view confidential information, modify settings, disable security controls, create accounts, access sensitive infrastructure, or move deeper into an organization’s technology environment.
Preventing privilege escalation requires granular permissions, secure application design, server-side policy enforcement, least privilege, logging, regular access reviews, and testing that specifically examines whether users can move beyond their intended authorization boundaries.
How AuthZ Supports Zero Trust Security
Zero Trust security is built around the idea that access should not be automatically trusted simply because a user or device is already inside a corporate network. Requests should be evaluated using identity, context, policies, and the sensitivity of the requested resource.
Authorization is therefore fundamental to Zero Trust architecture. Instead of granting broad network access after login, organizations can make more granular decisions about which resources and actions should be available to each identity.
These decisions may consider user identity, device health, authentication strength, resource classification, application sensitivity, location, risk signals, and session context. Permissions can also change when security conditions change.
This approach reduces reliance on traditional network boundaries. Whether someone works from headquarters, home, a mobile device, or cloud infrastructure, access decisions can remain focused on whether the particular request satisfies established security policies.
AuthZ in Cloud Computing
Cloud environments introduce huge numbers of resources, identities, services, APIs, and machine-to-machine interactions. Proper authorization determines which users and workloads can manage virtual machines, storage, databases, networking, secrets, applications, and administrative services.
Cloud providers commonly use IAM policies, roles, resource permissions, and service identities to manage this access. Small authorization mistakes can sometimes create large risks because cloud permissions may cover powerful infrastructure or enormous amounts of data.
Machine identities are especially important. Applications, containers, automation systems, serverless functions, and other workloads often need access to cloud resources, but these identities should receive only the exact permissions required for their tasks.
Organizations should regularly examine cloud permissions for unnecessary administrative privileges, unused roles, overly broad policies, stale service accounts, and public access. Strong AuthZ is a core part of maintaining secure cloud infrastructure at scale.
AuthZ in Microservices Architecture
Microservices architectures divide applications into smaller services that communicate with each other through APIs. This creates authorization challenges because access decisions may need to be enforced across many independent services rather than one centralized application.
A service receiving a request must understand whether the calling identity is allowed to perform the requested action. Depending on the architecture, this may involve user tokens, service identities, policy engines, API gateways, or service mesh technologies.
Authorization should not disappear simply because traffic originates from another internal service. Compromised workloads can sometimes use overly trusted internal connections to move between systems or access data outside their intended responsibilities.
Modern microservices security increasingly applies granular service-to-service authorization. Each workload receives an identity, and access policies define which services can communicate, which operations they may perform, and which protected resources they can reach.
How Authorization Decisions Are Enforced
Authorization systems often separate policy decisions from policy enforcement. A Policy Decision Point evaluates relevant rules and determines whether a request should be allowed, while a Policy Enforcement Point applies that decision where the resource is accessed.
This separation can help organizations use consistent authorization logic across different applications. Instead of every developer building completely independent access-control rules, applications can consult centralized or standardized policy mechanisms.
Enforcement still needs to occur reliably. Even the best authorization policy provides little protection if developers forget to call the policy engine, fail to protect a new endpoint, or allow alternative routes around the authorization check.
Organizations should therefore design authorization into application architecture from the beginning. Automated tests, centralized policies, code reviews, security testing, and monitoring can help identify situations where access rules are missing or incorrectly enforced.
Common AuthZ Mistakes to Avoid
One common mistake is granting permissions that are much broader than users actually require. Administrator roles are convenient, but assigning them unnecessarily increases the potential impact of compromised credentials, mistakes, and malicious activity.
Another problem is relying solely on frontend restrictions. Removing an administrative button from a webpage may improve the interface, but it does not prevent someone from sending a direct request to the underlying API if server-side authorization is missing.
Organizations also struggle with stale permissions. Employees change jobs, projects end, temporary access remains active, and abandoned accounts retain privileges unless access is regularly reviewed and removed when no longer necessary.
Inconsistent authorization across applications creates additional risk. One endpoint may enforce resource ownership correctly while another exposes the same information without equivalent checks, allowing attackers to search for overlooked paths around security controls.
Best Practices for Strong Authorization
Start with least privilege and deny access unless there is a legitimate reason to grant it. Permissions should be narrow, understandable, and aligned with real responsibilities rather than providing broad access simply for administrative convenience.
Centralize authorization policies where practical and consistently enforce them across applications, APIs, databases, and cloud services. Developers should avoid duplicating complex security logic in dozens of locations where rules can gradually become inconsistent.
Regular access reviews are equally important. Organizations should identify unused accounts, unnecessary administrator privileges, excessive API scopes, stale service credentials, old group memberships, and permissions that no longer match employee responsibilities.
Finally, test authorization as aggressively as authentication. Security teams should verify whether users can access another account’s resources, change protected identifiers, reach hidden endpoints, escalate privileges, bypass roles, or manipulate requests to obtain unauthorized access.
The Future of AuthZ
Authorization is becoming increasingly dynamic as organizations move away from simple static roles toward contextual security decisions. Identity, device health, risk level, data sensitivity, resource relationships, and behavioral signals can all influence whether access is granted.
Fine-grained authorization is also becoming more important for SaaS products and multi-tenant applications. Systems may need to model relationships such as organization membership, project ownership, document sharing, team hierarchy, and delegated administration.
Machine identities will further increase authorization complexity. Modern infrastructure contains enormous numbers of applications, workloads, agents, services, APIs, and automated processes that require carefully controlled access to other systems.
The direction is clear: authorization is moving from basic permission lists toward continuous, policy-driven access decisions. Organizations that understand who or what can access each resource—and why—will be better positioned to protect increasingly interconnected digital environments.
Final Thoughts
AuthZ is the security process that determines what an identity is permitted to do after its identity has been established. It controls access to applications, APIs, files, databases, cloud resources, administrative functions, and other protected digital assets.
Authorization can rely on roles, permissions, attributes, relationships, OAuth scopes, contextual signals, and centralized policies. Approaches such as RBAC, ABAC, PBAC, IAM, and Zero Trust provide different ways to implement these access decisions.
Strong authorization also requires more than simply assigning permissions. Organizations must enforce policies consistently, follow least privilege, protect resources at the server level, monitor privileged activity, and regularly remove unnecessary access.
As applications become more distributed and interconnected, AuthZ will continue to play a central role in cybersecurity. Authentication proves who an identity is, but authorization ultimately determines how much that identity can do once it enters the system.
Frequently Asked Questions
What does AuthZ mean?
AuthZ is an abbreviation for authorization. It is the process of determining whether a user, application, or service has permission to access a specific resource or perform a particular action.
What is the difference between AuthN and AuthZ?
AuthN means authentication and verifies who a user is. AuthZ means authorization and determines what that authenticated user is allowed to access or do within a system.
What are the main types of authorization?
Common authorization models include Role-Based Access Control (RBAC), Attribute-Based Access Control (ABAC), and policy-based access control. Organizations often combine multiple models for greater flexibility.
Does authorization happen before or after authentication?
Authorization usually happens after authentication establishes an identity. However, authorization checks can occur repeatedly during a session whenever the user attempts to access protected resources or perform sensitive actions.
Why is AuthZ important for API security?
AuthZ prevents authenticated API users from accessing data or functions outside their permissions. Strong API authorization helps stop broken access control, unauthorized data access, and privilege escalation.
