

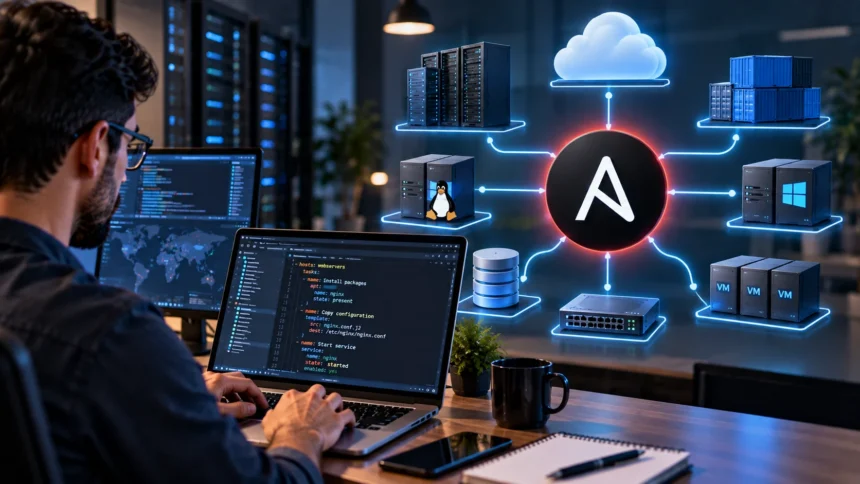
Ansible is an automation tool that helps IT teams manage servers, configure systems, deploy applications, and handle repetitive administrative work from a central location. Instead of logging into machines individually and repeating the same commands, administrators can describe what they want Ansible to do and apply those instructions consistently across many systems.
The platform is widely used in DevOps, cloud operations, configuration management, and infrastructure automation because it is relatively straightforward to understand and does not normally require agents on managed machines. Learning how Ansible works can help teams reduce manual work, prevent configuration differences, and manage growing technology environments more efficiently.
What Is Ansible?
Ansible is an open-source automation platform commonly used for configuration management, application deployment, server provisioning, and IT orchestration. Administrators define automation tasks in readable configuration files known as playbooks. Ansible then connects to managed systems and performs those tasks according to the instructions provided.
One major feature of Ansible is its agentless architecture. Many automation platforms require special software to be installed on every managed machine, but Ansible generally connects to Linux systems through SSH and can communicate with Windows environments through supported remote-management methods. This can simplify setup and reduce the amount of software maintained across infrastructure.
Ansible can automate everything from installing a package on several servers to coordinating complicated application deployments. Teams can use it on physical servers, virtual machines, cloud instances, and other supported infrastructure. Its flexibility makes it useful for both small environments and larger enterprise operations.
How Does Ansible Work?
Ansible typically operates from a control node where administrators store playbooks, inventory information, and configuration. The inventory identifies the servers or devices Ansible should manage. When a playbook runs, Ansible connects to those systems remotely and performs the specified tasks in the order defined.
A playbook can contain instructions such as creating users, installing packages, copying configuration files, starting services, or changing system settings. Instead of writing complicated scripts for every operation, administrators can use Ansible modules designed for common tasks. These modules provide a more structured way to describe the desired result.
Ansible generally works toward making a system match the state defined in the playbook. If a package is already installed, Ansible can recognize that no further installation is required. This behavior helps teams run automation repeatedly without unnecessarily performing the same changes every time.
What Are Ansible Playbooks?
Ansible playbooks are files that describe automation workflows using YAML, a human-readable data format. A playbook identifies which systems should receive changes and which tasks should be performed. Administrators can place multiple tasks together so Ansible carries out an entire configuration or deployment process consistently.
For example, a basic web server playbook could install a web server package, copy a configuration file, open the required network port, and start the service. Instead of completing each step manually on every machine, the team can run the playbook against all relevant servers at once.
Playbooks can also include variables, conditions, loops, handlers, and reusable components. These features allow teams to create automation that adapts to different environments without duplicating entire configurations. Well-organized playbooks become valuable documentation because they clearly show how important systems are intended to be configured.
Common Uses of Ansible
Configuration management is one of the most common Ansible use cases. Teams can define how operating systems, packages, services, users, permissions, and application settings should be configured. Applying the same automation across servers reduces the risk that one machine develops unexpected differences from the rest of the environment.
Application deployment is another important use. Ansible can copy application files, update configurations, restart services, and coordinate releases across multiple systems. Development and operations teams can use repeatable playbooks instead of relying on long manual checklists whenever a new application version needs to be deployed.
Ansible is also used for provisioning, security automation, cloud management, patching, network automation, and routine maintenance. Organizations can automate repetitive tasks such as user creation or software installation while creating more advanced workflows for larger infrastructure changes. The exact use depends on the team’s technical environment and operational requirements.
Main Benefits of Ansible
One of the biggest Ansible benefits is reduced manual work. Tasks that might require administrators to log into dozens of servers can be completed through a single automation workflow. This can save time while reducing human errors caused by forgetting steps or entering different commands on different systems.
The agentless design is another advantage. Teams do not generally need to install and maintain an additional Ansible agent across every Linux server they manage. This can make initial adoption easier and reduce the number of background services that must be updated and monitored throughout the infrastructure.
Ansible playbooks are also relatively readable compared with highly specialized programming languages. Operations teams can review automation instructions and understand what changes will occur. This supports collaboration, documentation, peer review, and version control while making infrastructure knowledge less dependent on one administrator remembering every manual procedure.
Ansible for Configuration Management
Configuration drift occurs when servers that were originally identical gradually develop different settings over time. One administrator may install an additional package, another may change a configuration manually, and eventually systems behave differently. These inconsistencies can make application failures difficult to diagnose and reproduce.
Ansible helps reduce configuration drift by allowing teams to define an approved system state through playbooks. The same configuration can be applied repeatedly across relevant machines. If a setting changes unexpectedly, automation can help restore the server to the configuration the organization expects.
This approach is particularly valuable for environments containing many similar servers. Instead of treating each machine as a unique system, administrators can manage groups of infrastructure consistently. Standardization makes patching, security reviews, troubleshooting, and application deployment more predictable across development and production environments.
Ansible for Application Deployment
Application deployments often involve more than copying new software files. Teams may need to update packages, change environment variables, modify configuration files, migrate databases, restart services, and verify application health. Performing these steps manually can become risky as the number of servers grows.
Ansible allows teams to turn deployment procedures into repeatable playbooks. The automation can apply tasks in a controlled order and target specific groups of servers. This reduces dependence on administrators remembering a complex sequence of commands during every software release.
Organizations can also integrate Ansible with CI/CD systems so approved application versions trigger automated deployment workflows. Testing and approval steps can happen earlier in the pipeline, while Ansible handles environment configuration or release tasks. This helps development and operations teams create a more consistent path from tested software to production.
Ansible and Windows Automation
Ansible is often associated with Linux, but it can also automate many Windows administration tasks. Teams can manage users, services, files, software packages, registry settings, updates, and other supported Windows configurations. This can help organizations apply standardized automation across mixed operating system environments.
Windows administrators still need to configure the appropriate remote-management connectivity and permissions before Ansible can manage those systems. Once the connection is working, teams can create playbooks for repetitive tasks rather than handling each Windows machine individually. This can be particularly useful across larger fleets of employee systems or servers.
Administrators who work heavily with Windows often use additional productivity utilities alongside automation tools. For everyday tasks involving copied commands, file paths, or configuration snippets, clipboard managers can also simplify repetitive desktop workflows. These tools serve a different purpose from Ansible but can complement an administrator’s daily workflow.
Ansible vs Terraform
Ansible and Terraform are both used in infrastructure automation, but they typically focus on different layers. Terraform is commonly used to provision infrastructure such as cloud networks, virtual machines, databases, and storage. Ansible is frequently used to configure operating systems and software after those infrastructure resources already exist.
For example, Terraform might create ten cloud servers and their networking resources. Ansible could then connect to those servers, install application packages, configure services, create user accounts, and deploy software. Using the tools together can create a complete workflow from infrastructure provisioning through system configuration.
The distinction is not absolute because their capabilities can overlap. However, teams generally achieve cleaner automation when each tool is used for the tasks it handles most naturally. Understanding whether a problem involves infrastructure provisioning or system configuration can help determine which platform is more appropriate.
Ansible Roles and Reusable Automation
Ansible roles help teams organize related automation into reusable components. Instead of placing hundreds of unrelated tasks inside one enormous playbook, administrators can separate configurations into roles for databases, web servers, monitoring, security, or other infrastructure functions. This makes large automation projects easier to understand.
A role can contain tasks, variables, templates, handlers, and files needed for a particular configuration. The same role can then be reused across several applications or environments. Teams can change input variables while maintaining the same core automation logic, reducing repetitive configuration.
Reusable roles also help organizations create internal standards. A security team might develop an approved server-hardening role that project teams use whenever new infrastructure is configured. Centralized reusable automation can reduce duplicated work and make important changes easier to distribute consistently across many systems.
Ansible Security Best Practices
Automation tools often require powerful permissions, so protecting Ansible environments is essential. Organizations should limit who can modify playbooks, inventories, and credentials used to access production infrastructure. Version control and peer review can help ensure that significant automation changes are examined before they are executed.
Passwords, API keys, certificates, and other secrets should not be placed directly inside ordinary playbooks. Secure secret-management features can help protect sensitive values while still allowing automation to access them when necessary. Repository access should also be restricted so confidential infrastructure information does not become publicly exposed.
Teams should test automation in lower-risk environments before running major changes across production systems. A mistake inside a playbook can be repeated across many servers very quickly. Careful testing, backups, access controls, and gradual rollouts help organizations gain the benefits of automation without allowing one incorrect configuration to create widespread disruption.
Common Ansible Challenges
Ansible is relatively approachable, but large automation projects can still become complicated. Playbooks may grow difficult to maintain when teams duplicate tasks, use inconsistent naming, or place unrelated automation into the same files. Clear structure and reusable roles can prevent configurations from turning into an unmanageable collection of instructions.
Performance can also become a consideration when managing very large numbers of systems. Remote connections and sequential tasks may require optimization depending on the infrastructure size and workflow. Teams should organize inventories and automation carefully rather than assuming the same design will work equally well from ten servers to thousands.
Another challenge is relying too heavily on automation without understanding the systems underneath it. Ansible can install packages or modify network settings, but administrators still need knowledge of operating systems, applications, networking, and security. Automation makes technical work faster; it does not remove the need to understand what the changes actually do.
Ansible Best Practices
Keep playbooks focused and readable. Clear task names, logical structure, reusable roles, and useful documentation make automation easier for teammates to understand. Avoid creating unnecessarily complex workflows when several simple and predictable tasks can achieve the same result more safely.
Store Ansible configurations in version control so changes have a documented history. Important updates should go through peer review, particularly when they affect production systems or security settings. Teams can compare new versions with previous configurations and identify when potentially risky changes were introduced.
Design playbooks to be idempotent whenever possible, meaning repeated execution should produce the same desired state without causing unnecessary changes. Test workflows before production deployment and monitor the results afterward. Reliable automation should make infrastructure more predictable rather than simply execute commands more quickly.
Simple Ansible Examples
Imagine a company with twenty web servers that all require the same software package. Instead of logging into each machine separately, an administrator can create an Ansible playbook specifying that the package must be installed. Running the playbook applies the desired configuration across every targeted server.
Another example involves employee account management. A playbook can create approved user accounts, assign group memberships, configure permissions, and distribute required access keys across infrastructure. When policies change, administrators can update the automation and apply the new configuration consistently rather than editing each system manually.
Ansible can also manage application configuration files. Teams can create templates containing variables for development, staging, and production environments. Ansible generates the appropriate file for each system and restarts affected services when necessary, providing a repeatable workflow that reduces manual configuration differences between environments.
Conclusion
Ansible is an automation platform that helps teams configure systems, deploy applications, manage infrastructure, and reduce repetitive administrative work. Its agentless architecture and readable playbooks make it approachable for many operations teams. Administrators can define desired configurations once and apply them consistently across multiple systems.
Its major benefits include reduced manual effort, better configuration consistency, reusable automation, faster deployments, and easier infrastructure management. Ansible works particularly well for configuration management and system administration while complementing provisioning tools such as Terraform. It can also support Linux, Windows, cloud, network, and mixed infrastructure environments.
Successful Ansible adoption requires thoughtful playbook design, strong security, testing, version control, and technical understanding of the systems being managed. Automation should simplify operations rather than create hidden complexity. When implemented carefully, Ansible can help DevOps and IT teams manage larger environments with greater speed and consistency.
FAQs
What is Ansible used for?
Ansible is commonly used for configuration management, software installation, application deployment, patching, user management, cloud automation, security tasks, and coordinating repetitive administrative work across multiple systems.
Is Ansible a DevOps tool?
Yes. Ansible is widely used in DevOps because it automates system configuration and deployment tasks, integrates with CI/CD workflows, and helps development and operations teams maintain consistent infrastructure.
Does Ansible require coding?
Ansible usually requires writing YAML playbooks rather than traditional application code. Basic automation can be relatively simple, although advanced workflows still require technical knowledge of systems, variables, conditions, templates, and infrastructure.
Is Ansible better than Terraform?
Neither is universally better. Terraform is commonly used for provisioning infrastructure, while Ansible focuses heavily on configuration management and application deployment. Many DevOps teams use both tools together.
Does Ansible need an agent?
Ansible is generally described as agentless because it usually connects to managed systems through existing remote-management technologies rather than requiring a dedicated Ansible agent on every machine.
